DanBlake
Joined 17 years ago
Karma
4,129
Submissions
737
Member since
Nov 26
harknesslabs.com
View on Hacker NewsJoined 17 years ago
This app was created to answer questions that are not possible to easily answer now, like "What are my top 10 restaurants in miami" or "when was the last time I was at the dentist". While perhaps the audience for such data isnt as large as social platforms, I believe that there is enough utility in this for it to succeed.
The app itself is built in react (so android version coming in next few weeks) and makes use of custom geofence zones to accurately (in testing, more accurate than any other app in the ios app store) get your location and track your path with minimal battery drain of about 3-5% per day. All this done in the background.
Right now, the analytics options are just getting started but we are building out a full suite of detailed 'drill downs' for people to explore their data, even with the ability for you to write your own queries if you choose.
Id appreciate any comments or criticisms, be as harsh as you want- This app was a huge undertaking and if there are shortcomings I want to hear them.
The beauty line doesnt work, because then platinum shouldnt have any serious value despite its rarity (it just looks like silver basically)
The industrial value is laughable, but read comments below/above to debate that more at length.
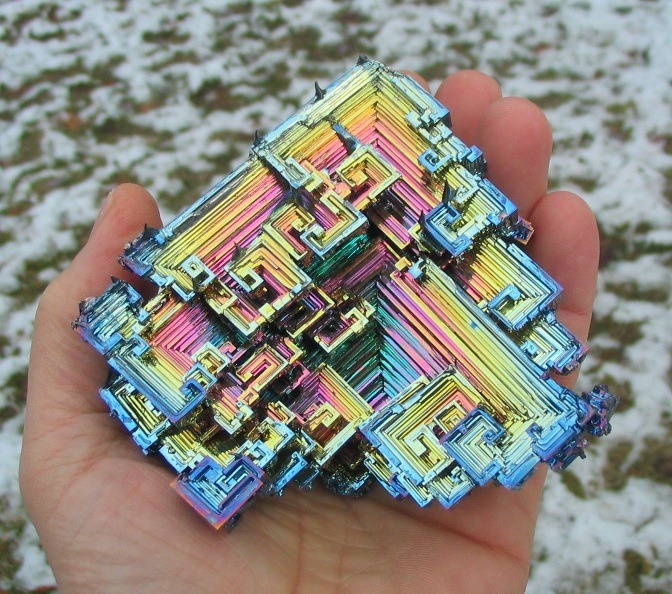
The scarcity line doesn't work, because you have elements like bismuth which are also (Arguably) more beautiful than gold https://66.media.tumblr.com/61ce390242a79a767772d4b2027eb902... but command prices far less despite being .025 vs .0031 on the PPM abundance on earth. Or even look at ruthenium which has a similar look to platinum and is even rarer than gold. Did I mention it also goes for about 400 an ounce? Quite a savings over gold.
The only thing that makes sense is that we as a collective have decided gold has value of X.
If you want to go the modern (better) route, enterprise equipment such as ubiquity or cisco with strict rules are likely your best bet. The budget option being a openwrt install with one of their recommended routers
In fact, I bet many of them are so frustrated with the errors of nothing working that they dont even attempt to sign up for things with the email most times.
Honestly, if you decide to use a email like n@ai you already know what to expect. Most services wont let you sign up, And even if they do most will likely incur errors in the application when you attempt to do things.
In reality, while it may be 'in spec' to use such a email, we can all hope that edge cases that allow it are changed and the legacy 'rules' that allowed it in the first place phased out completely.
So, in practice in the 'real world'- n@ai is not a valid email address and never will be. If I create a web application you can bet your bottom dollar I wont allow it and I will create less work for myself by doing so.
Picture of what I kind of mean here : https://pbs.twimg.com/media/Diylx-0X4AIjrqO.jpg
*edit- slide #2 and #3 are backwards. The passwords are stored on the USB device, if that wasnt clear. Master password allows you to view password titles and essentially 'unlock' the usb device. However, every action needs to be confirmed one by one. So for instance, you could in theory export 'all' passwords in one shot, but it would present you with that prompt on the device itself.
However, Checking the new yorkers revenue shows around 200 million/yr, I definitely did not expect that and likely means it can easily support a union. (unless the new yorker is loaded with debt, which it might be)