kronxe
Joined 6 years ago
Karma
32
Submissions
18
Member since
Aug 22
github.com/bilalonur
View on Hacker NewsJoined 6 years ago
Font Engine is currently in an experimental version, so some results may not meet your expectations. These can only be improved with your feedback.
ProductHunt page: https://www.producthunt.com/posts/gradient-palette
Instagram: https://www.instagram.com/tasarlalabs/
By the way, I mentioned N=NP due to show probably in a few years there is solution of this problem and maybe the end of the bitcoin [1].
As your claim about brute-forcability, I want to say quantum computing is experimental right now but there is working machine and proccesing units of them. In other words, it is not only theoretical and Quantum computing age probably allows to crack these all algorithms probably mine as well with Quantum AI. However, in my opinion, if people do not know how your algorithms work, the attacking possibility is dramatically decreases.It is more difficult to target something unknown.
[1] https://gizmodo.com/if-you-solve-this-math-problem-you-could...
Also, I recommend you to read Google's quantum paper and quantum attacks on some sort of cryptography things.
If we think about today, we cannot catch up new techs, we should think about future. That is why technology is growing exponential.
> Your claim suggests that you are not familiar with cryptography at all. Modern cryptographic algorithms are parameterized with keys in a way that knowing the algorithm doesn't give adversaries much hint---you just have to keep keys safe. By comparison knowing that your algorithm is in use allows the complete decryption.
Have you got an experience in data encryption for databases or related ? My point is your function may used by other people, for example: If a hacker reached db of website, and tried to find the keys of encryption. He can make brute force trial to accomplish it or some analysis. There is lots of field that used cryptography like e2e encryption in communication applications or cryp. hash functions like md5 in databases. This field is very broad, it does not focus on just one subject.
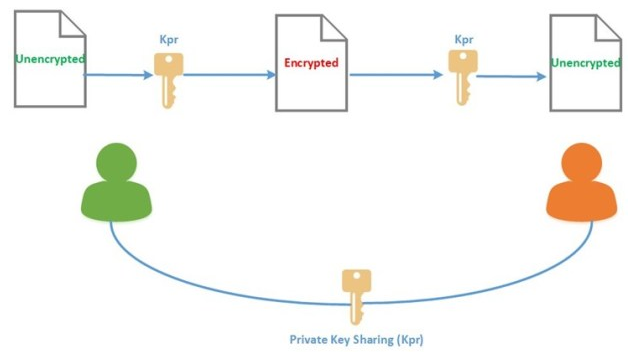
[1] https://miro.medium.com/max/1272/1*sc0fhLXdwc2WRzGRDAfkcQ.pn...
I think you are not familiar with the cryptography concepts in general trends because today the most of data breaches become dangerous if the encrpyted part decrypts by the hackers, so that is why we should avoid typical approaches.
Also, your question about complexity, I am sorry but I can not understand. If you have an important data, you should protect it by an well-developed algorithm.
Also, my other point is it is not an stable, constant algorithm. Everyone may have different TBCAs for their specific purposes but there should be generic ideas like human names or in an online game if you give '~' for 'GG' , you can save too many locations in memory. For a chat application, if you change 'hello' to some two bytes and you save both memory and time (because transmission of long bytes takes more than compression process probably if you dont have a huge dictionary).