UnquietTinkerer
Joined 12 years ago
Karma
95
Submissions
30
Member since
Nov 29
Joined 12 years ago
In all seriousness, anonymous sum types would be quite nice. It would make it easier to be precise about return values in situations where `Optional` and `Result` are not sufficient.
The problem with checked exceptions (well, one of the problems) is that the full set of error conditions a function might encounter is often _too_ detailed. Encoding them all into the type signature of every function can be a lot of work, and quite brittle to minor internal changes. So most code bases will still need a catch-call error type that gets bubbled up to a generic handler somewhere.
However, I found that the path logic inscrutable and frustrating. The creeps take a random path when they reach some intersections (I think? There was no explanation and no obvious pattern). Success in stage 8 seems to depend entirely on luck. I would expect a game themed around computer logic to be more deterministic.
The writer pretty clearly has an axe to grind with the city, the sanctions, the war, and a lot more (read some of his other comments). His conclusions might turn out to be true, but I don't think he cares if they are or not.
When you frame it as an investment question, the implication is that if either person walks away then they can be replaced by a third party who is willing to stake the cash. Since it is easier to replace someone when their stake is lower, the person putting up the $2k has less leverage in this case.
If you explicitly limited the investment to two specific people (imagine a crazy term in a will or something), then I think you'd end up back with a $7k/$5k split.
People (including me) _hate_ memorizing things and would probably write an assigned password down, but isn't it better to expose passwords to nosy coworkers than to the whole internet, as is so often the case with weak or reused passwords?
https://utio.net/demos/box_drawing.png
I only mention this because I've used these to decorate tables in my own notes in the past. It's not really worth the trouble, but I remembered being impressed with how nice these characters looked at the time.
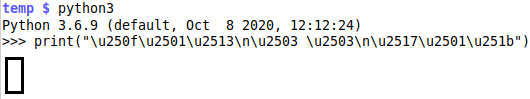
If anyone else wants to try it, paste this into a python REPL:
print("\u250f\u2501\u2513\n\u2503 \u2503\n\u2517\u2501\u251b")It's amusing that the Go app was built in a highly controlled environment, while the kernel was built on some random laptop (and was compromised).
It seems like the attack was highly specialized, so I assume that the PII being handled by this client/victim is pretty valuable?
[Slides] https://millcomputing.com/blog/wp-content/uploads/2018/04/20...
[White Paper] https://millcomputing.com/blog/wp-content/uploads/2018/01/Sp...
I haven't read the paper yet; hopefully it offers more detail than the talk does because I am still confused about how the Mill avoids cache pollution from speculative loads.
EDIT: Here is my attempt at a summary of the relevant bits of the whitepaper:
The Mill is immune to Meltdown for the same reason AMD et al. are; it does permission checks before loading rather than in parallel and thus the load faults before going to memory.
The Mill is immune to Spectre because "Current Mill configurations will [speculatively] issue, and revoke, a maximum of two instructions. Revocation includes all cache and other micro-architectural side effects."
Neither of those points is covered in the talk. I don't know enough about the subject to judge, but the arguments in the paper seem a bit glib. I'd like to hear from an expert on the subject.
    #! /bin/sh
    # This is a bit hacky: we use the -i flag to force the interpreter into
    # interactive mode after the initial commands are executed.
    # The "proper" way to do this is probably to set up a PYTHONSTARTUP file
    # and put the initial commands in there.
    exec ipython3 --no-banner --no-confirm-exit -i -c '
    from math import *
    import random
    import sys, os, platform
    print("== IPython %s Calculator REPL ==" % platform.python_version())
'That is not to say the page is well-designed or pretty - it is hideous. But lazy loading would make it strictly worse by adding js parse+eval latency on top of the loading time for the images.