

billyhoffman
Joined 16 years ago
Karma
3,831
Submissions
643
Member since
Jun 10
Joined 16 years ago
I recently built a Gemini client for people who like GUI's more than TUI's, and want a native macOS app
* Don't like menubar apps? you you can run it as a normal app
* Don't like GUIs? Now you can run it on the command line
Just look at that Changelog:
You account is not even 3 months old. In that time you made 6 submissions, all of them appears to be to your own work. You have only commented 9 times, with almost all of them being comments about your work.
Its a CMS, designed from scratch, for a serverless world. It has a stricter, well defined API that plugins are forced to use instead of directly calling/overriding core functionality like in WP. But that benefit comes with a CMS that's built on top of, and seems to prefer, a ton of CF proprietary capabilities (D1 Databases, R2 for image/media storage, their workers for running things).
The web need less consolidation on CF, not more.
1- EmDash plugins are written in TypeScript, not PHP
2- EmDash plugins have a specific permissions model, where they need to explicitly request access to certain things.
3- WordPress plugins just invoke things. EmDash plugins have a defined API you use to talk to different capabilitites
4- Those capabilities are totally different, and at a different abstraction, than what WordPress provides.
Beyond the look of the admin interface and publishing flow, I don't see how this is a "Spirtual Successor" to WordPress at all. Its a CMS, designed from scratch, for a serverless world, using CF proprietary capabilities (D1 Databases, R2 for image/media storage, their workers for running things).
https://sixcolors.com/post/2026/03/apple-introduces-colorful...
Single Core performance: the A18 Pro is faster than an M3!
Multi Core performance: The A18 Pro is essentially the same as an M1.
This balance seems right for the target market of a $599 laptop.
The price point was designed to get customers who would not pay for a $1000 computer into using a Mac. Sourcing those 2020 era M1 components, screens, etc, let alone M1's, was probably becoming a problem in 2026.
The Macbook Neo is a modern way to meet that price point. The video ad is more instructional about what macOS is, and how it would work with an iphone the customer may already have.
It does very basic Apple Intelligence (they show the photo editing in the video), but this is not for running models locally (they even show the ChatGPT native app and say "runs all your favorite AI apps")
People complaining about the 8 GB limit are missing who the target market is for this machine. Its a Mac, for $599!
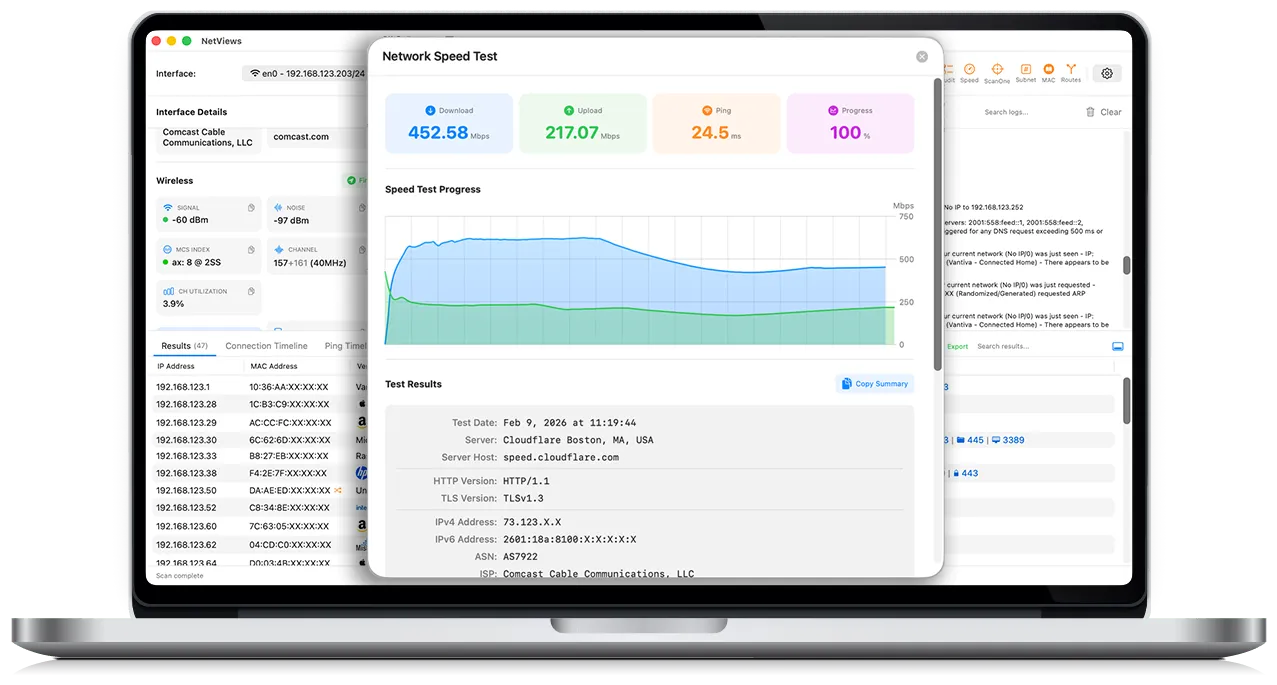
Minor bug: I tried opening the WebP screen shots in another tab so I could zoom and see them more clearly, and it does not work. Chrome renders the WebP image data as text, and Safari prompts you to download it. This appears to be because the web server is not returning a `Content-Type` header for these URLs:
curl --head https://www.netviews.app/_astro/ss7.D8bYvHF6_1awjYx.webp
EDIT: Fixed! I see a Content-Type header now
https://www.reddit.com/r/torrents/comments/vc0v08/question_a...
The solution is to use one of the several IA downloader script on GitHub, which download content via the collection's file list. I don't like directly downloading since I know that is most cost to IA, but torrents really are an option for some collections.
Turns out, there are a lot of 500BG-2TB collections for ROMs/ISOs for video game consoles through the 7th and 8th generation, available on the IA...
gemini://kennedy.gemi.dev
There are ~4K hosts and ~1M documents/images/files which make for nice playground with experimenting with crawlers, indexers, and more. Its a nice hobby. Lots of primarily static sites, and CGI is used to add some interactivity:
gemini://gemi.dev/cgi-bin/moon.py
PCI DSS is the data security standard required by credit card processors for you to be able to accept credit card payments online. Since version 1.0 came out in 2004, Requirement 4.1 has been there, requiring encrypted connections when transmitting card holder information.
There’s certainly was a time when you had two parts of a commerce website: one site all of the product stuff and catalogs and categories and descriptions which are all served over HTTP (www.shop.com) and then usually an entirely separate domain (secure.shop.com) where are the actual checkout process started that used SSL/TLS. This was due to the overhead of SSL in the early 2000s and the cost of certificates. This largely went away once Intel processors got hardware accelerated instructions for things like AES, certificates became more cost-effective, and then let’s encrypt made it simple.
Occasionally during the 2000s and 2010s you might see HTML form that were served over HTTP and the target was an HTTPS URL but even that was rare simply because it was a lot of work to make it that complex instead of having the checkout button just take you to an entirely different site
This was the opposite of a professional response:
* Official communication coming from a Gmail. (Is this even an employee or some random contractor?)
* Asked no clarifying questions
* Gave no timelines for expected fixes, no expectations on when the next communication should be
* No discussion about process to disclose the issues publicly
* Mixing unrelated business discussions within a security discussion. While not an outright offer of a bribe, ANY adjacent comments about creating a business relationship like a sponsorship is wildly inappropriate in this context.
These folks are total clown shoes on the security side, and the efficacy of their "fix", and then their lack of communication, further proves that.
But when I attended the first day, I learned that Gatech's online registration system had truncated the class title. The full title was "Modern Authors: James Joyce", and I was the only engineering student in a semester long class about James Joyce, which I had to take it and pass in order to graduate.
It was... pretty good actually.
Portrait of an Artist as a Young Man was enjoyable, as were his short stories. His style was unlike anything I had read before and it was musical in a way. However, I found Ulysses impenetrable: It rambled, and was difficult to understand what was even being described in the text, let alone the significance of it. Mostly it was just strange. Thankfully the majority of your grade was based participating in class discussion. Talking about it, seeing how confused everyone else was, and trying to make sense of it all together was a fun way to spend an afternoon in Skiles.
I'm pretty findable.